Bitcoin RSI bullish divergence draws 2022 comparisons as analysis weighs new price trend

Bitcoin price analysis eyes the potential end of its current macro downtrend based on weekly RSI signals.
 kamal
Bitcoin price analysis eyes the potential end of its current macro downtrend based on weekly RSI signals.
Monday’s $33.5 million was the largest single-day inflow since December, pushing cumulative net inflows to a record $1.22 billion and trading volume to $166.8 million.
Digital assets are among five sectors in a campaign Treasury called an “Economic D-Day,” alongside technology, gold, aviation and shipping.
Thailand’s SEC opened consultations on local Bitcoin and Ether ETF rules and qualification standards for foreign digital asset custodians.
The bank plans tokenized money market fund settlements in the fourth quarter as HKDAP expands its phased rollout into conventional banking.
The $1.8 trillion manager is putting its onchain money market fund on the Hong Kong exchange’s Earn channel.
There was a time when enterprises worried about perimeter defenses- safeguarding their supply chain security against outside threats. Today, the rapid growth of SaaS applications has created a more complex challenge: a web of tools, APIs, OAuth tokens, webhooks, and automated workflows connecting finance, HR, operations, customer service, and analytics. All it takes is one … Read more
Alabama’s attorney general issued a subpoena to OpenAI on Monday as part of an investigation into how one of its AI agents escaped a supposedly secure testing environment and autonomously hacked another company last month. The investigation seeks to determine whether OpenAI’s safety practices violated state consumer protection laws and pose a risk to Alabama … Read more
Mirage2FA is an active phishing-as-a-service toolkit built to steal Microsoft 365 credentials and authenticated sessions through Adversary-in-the-Middle (AiTM) attacks. ANY.RUN research shows that 63.7% of identified victims are in the US, with Technologies, Manufacturing, and Education among the most targeted industries. The operation has generated thousands of compromise events between 2024 and 2026, including stolen session cookies, passwords, and … Read more
While one may be tempted to believe that venture capital money has exited crypto in a big way this year, that narrative is not entirely correct. To elaborate, DeFi, a category that was the poster child for massive investments just a year or two ago pulled in around $654 million over the first half of … Read more
Treasury says Ivan Obukhov processed over $100 million in crypto for IRGC-QF oil sales since 2023.
Galaxy Research’s latest tally shows that more than half of 221 Coldcard hack victim reports involved individual losses exceeding 1 Bitcoin.
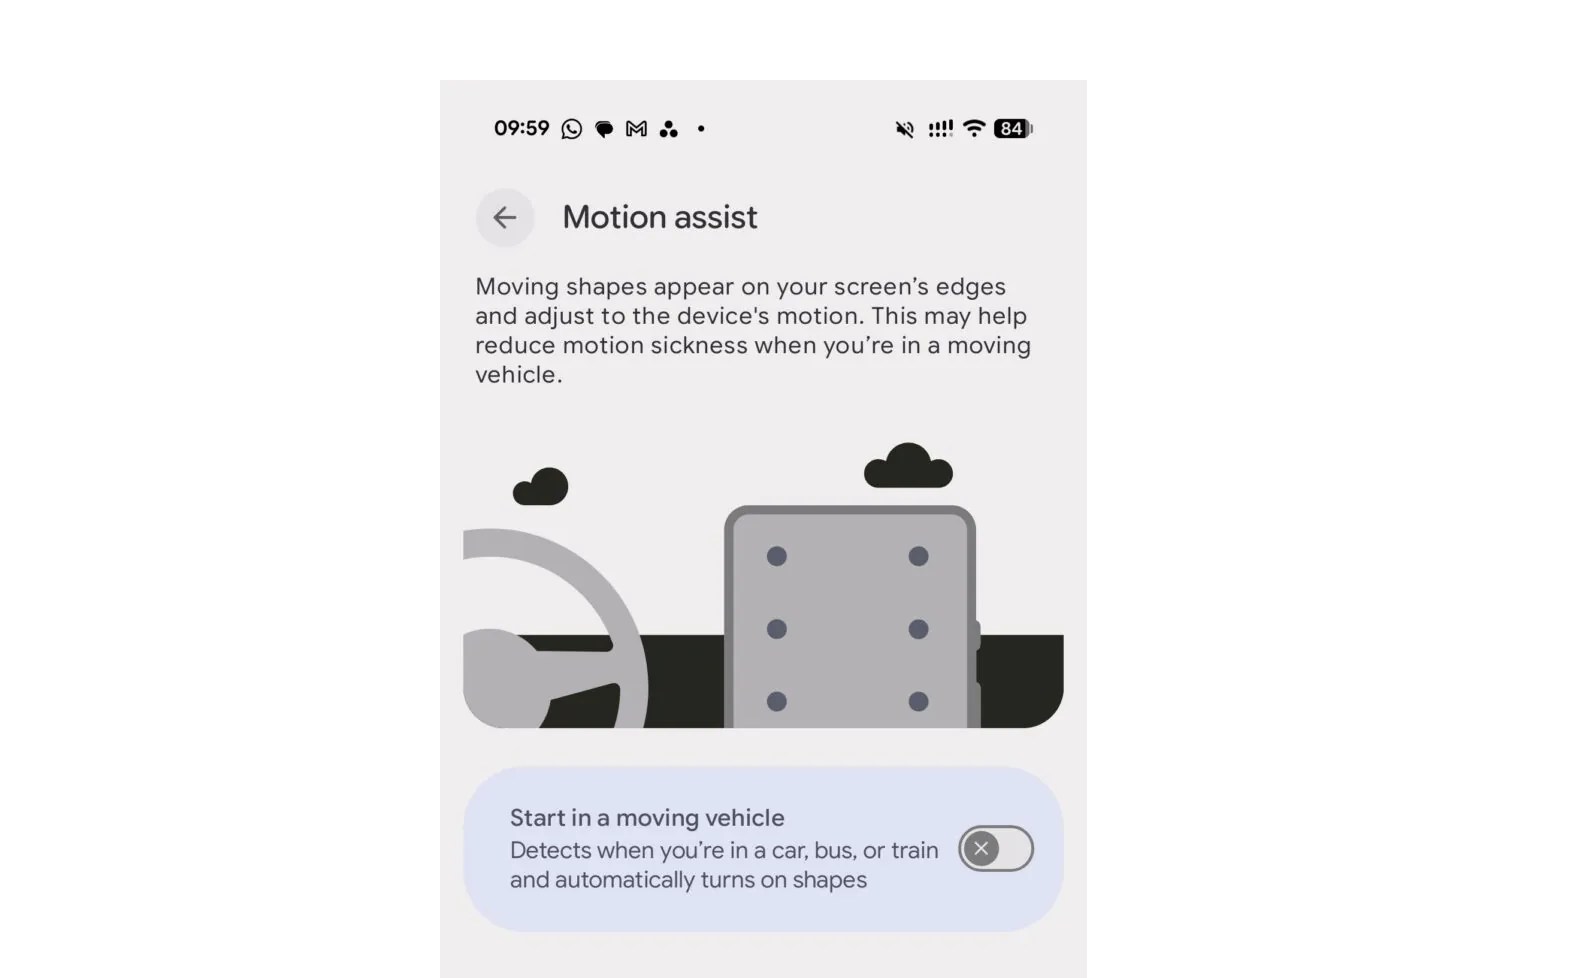
Motion Assist as found in Android 17’s settings. | Image: Android Authority (cropped by The Verge) Google is rolling out a new Android feature that’s been proven to reduce, or even eliminate, motion sickness when using a phone inside a moving vehicle. Dubbed Motion Assist by Google, it’s very similar to Apple’s Motion Cues, first … Read more
A federal jury convicted Brent Kovar of wire fraud, mail fraud and money laundering after he took $24 million from at least 400 investors.
Tokenized U.S. treasury and money market funds are one of the fastest-growing segments in the digital asset markets, growing fifteenfold in two years.
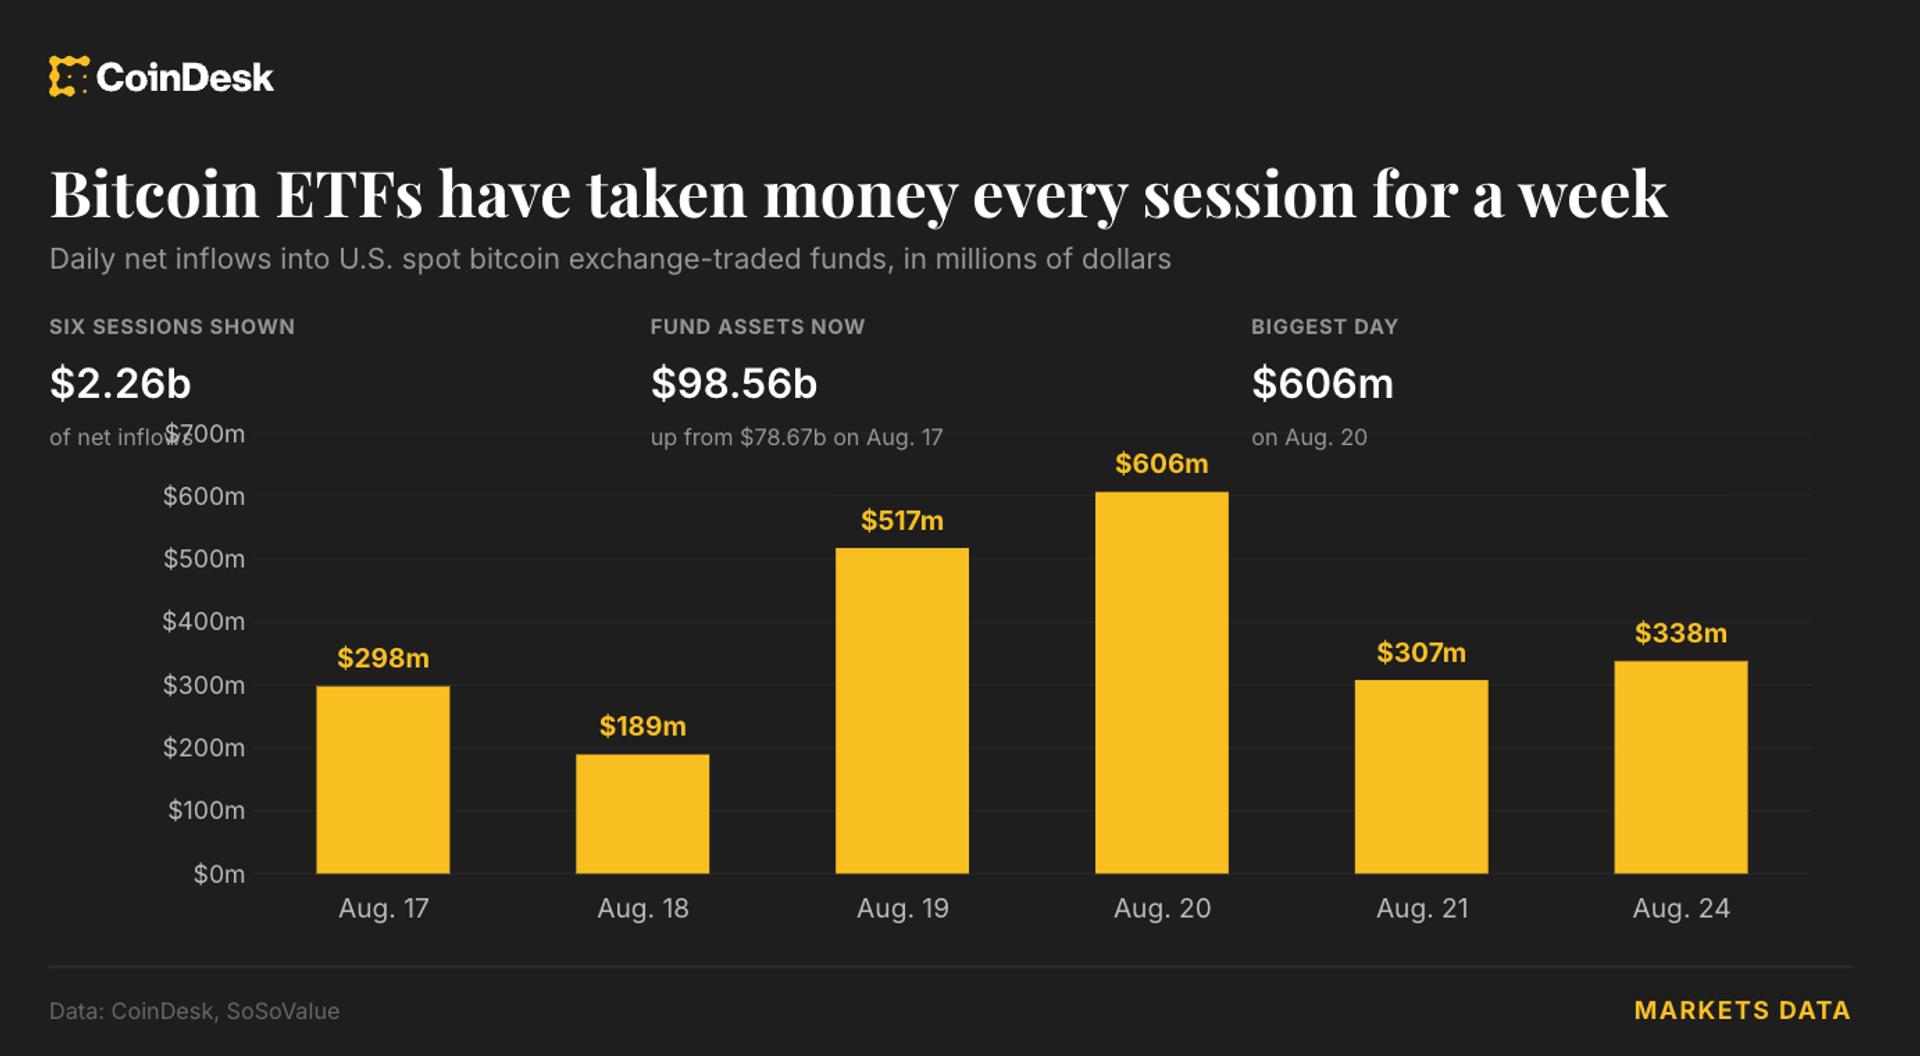
Spot bitcoin funds took in $337.56 million on Aug. 24, extending an unbroken run of inflows that has now put real money behind a rally that started with a short squeeze.
Bitcoin ETFs have drawn $2.26 billion over six trading days, while year-to-date net outflows have narrowed to about $2.57 billion.
The billionaire investor argues the intervention removes a vital check on government borrowing and fiscal accountability while markets remain the better judge of prices.
The Ethereum-compatible blockchain wants users to be able to replace the keys controlling an account without changing its address, opening the door to passkeys, recovery tools and post-quantum security.
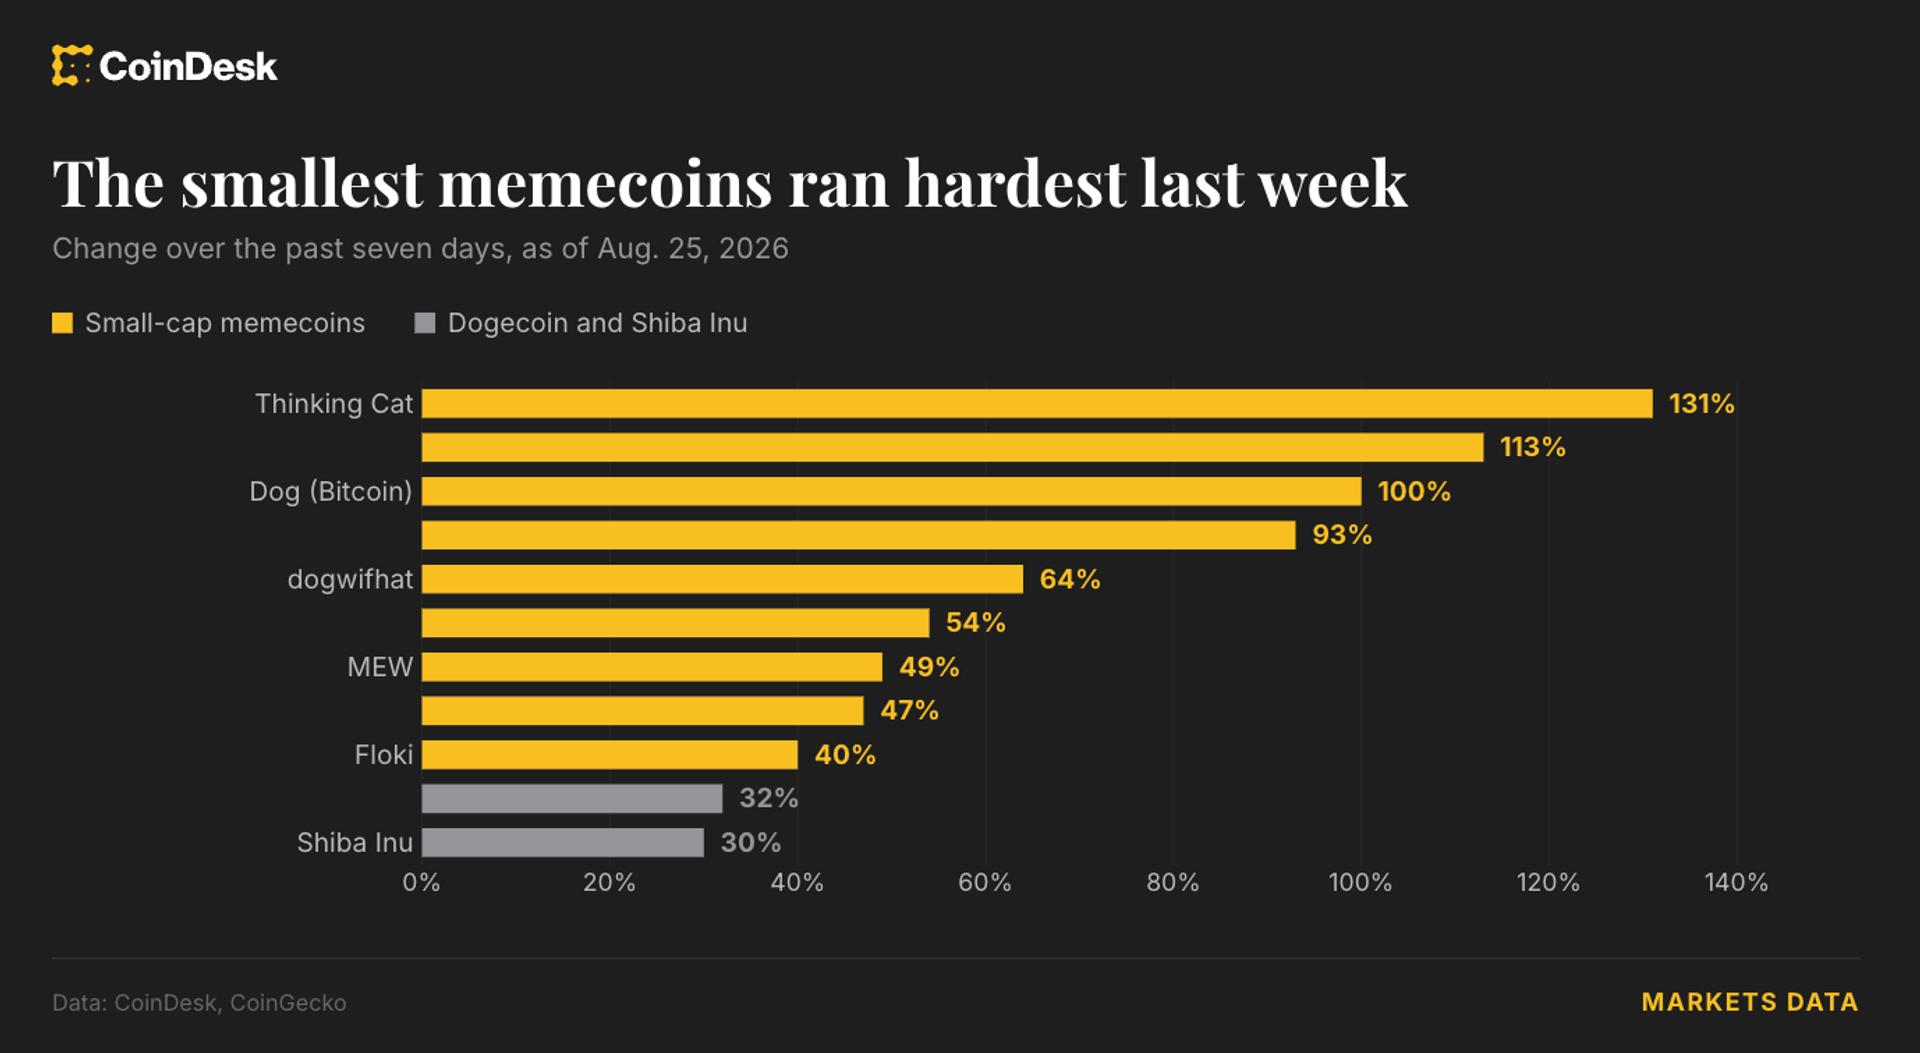
Robinhood Chain-based Cash Cat jumped more than 50% in a day, while several smaller animal-themed tokens have gained between 50% and 130% over the past week.
Traders are spending millions to position for further Bitcoin upside after its staggering rally to $80,000, though demand for downside protection remains firm, according to Laevitas.
The US Treasury expanded sanctions to Iran’s digital asset sector, alleging a UAE-based broker processed over $100 million in crypto for oil sales.
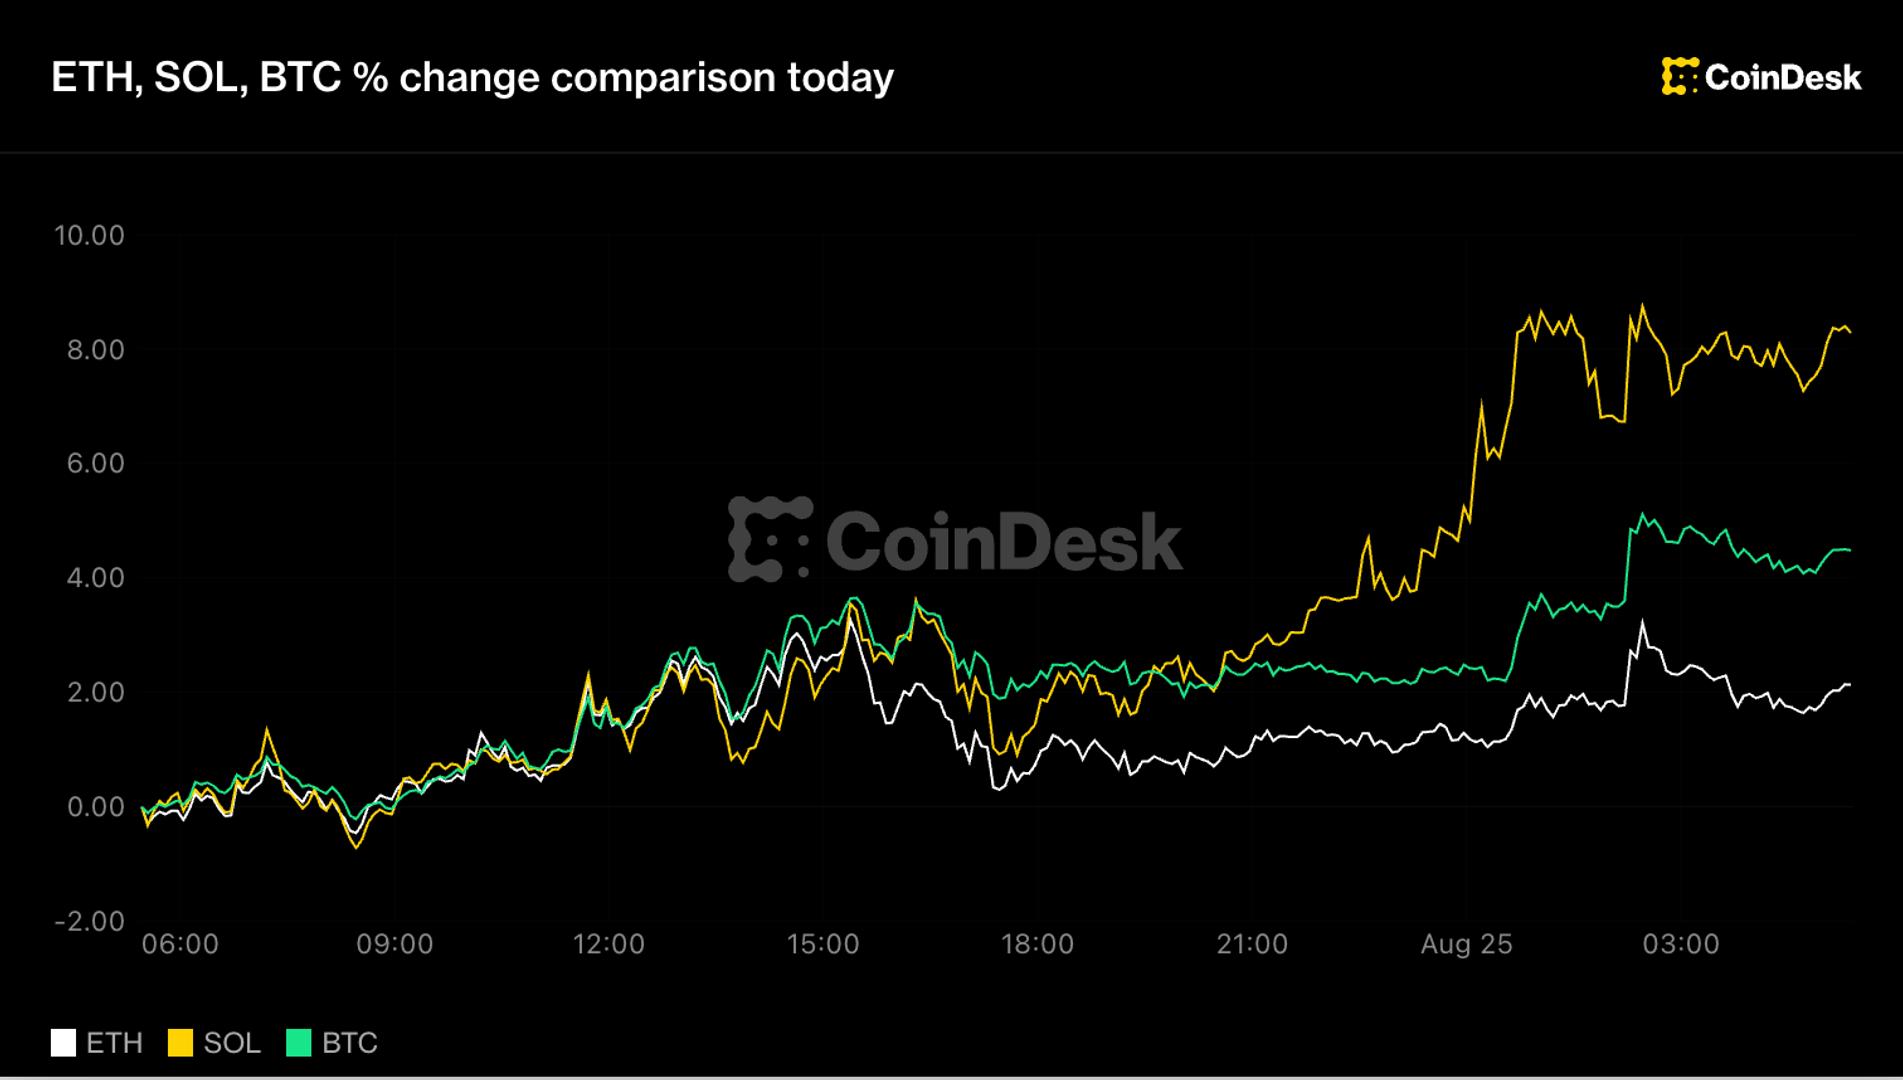
BTC is up more than 25% on the week after Treasury’s bond-buyback expansion sparked a rally, while Solana led majors Tuesday as validators vote on proposals to slow new SOL creation and raise daily burns.
Claude Opus 5 is Anthropic’s latest flagship, released on July 24. Anthropic describes it as delivering frontier intelligence at half the price of Claude Fable 5, and calls out one capability in particular: Opus 5 is unusually good at verifying its own work and catching logical flaws while it plans. That’s an interesting claim to … Read more
I remember the exact moment I realized we had a problem. It was a Tuesday afternoon, and our team had just integrated an LLM into a customer-facing support chatbot. The model was brilliant : fast, articulate, and impressively knowledgeable. Everything worked flawlessly in staging. We shipped it to their (luckily) QA environment on a Friday … Read more
BNB Chain activates the Pasteur hard fork on BSC, closing bridge and validator security gaps while targeting greater transaction capacity.
Airbound’s ultra-lightweight approach to drone delivery has attracted backing from Greenoaks, DoorDash, and Silicon Valley investor Lachy Groom.
Comments
Asia’s biggest crypto hubs are locked in a tax-cut arms race, while Ripple will help Korea’s Jeonbuk Bank move money across borders.